10 Email Privacy Tips Everyone Should Know

In This Article
Think about what sits in your inbox right now. Password resets, bank statements, medical records, legal documents. Your inbox is the master key to everything you do online. Protecting your email privacy isn’t optional anymore, it’s foundational.
These ten email privacy practices range from quick wins you can implement in five minutes to deeper habits that protect you over the long term.
1. Use Different Emails for Different Purposes
The best thing you can do for email privacy is to stop using one address for everything. Compartmentalization limits the blast radius of any single breach and keeps marketing spam out of your important inboxes.
The ideal setup has at least three tiers. A private, encrypted email account for personal correspondence and sensitive accounts like banking. Your work email for professional communication. And disposable email addresses for online signups, free trials, and one-time interactions.
| Tier | Which email | Use it for |
|---|---|---|
| 1 | A private, encrypted email account | Personal mail, banking and other sensitive accounts |
| 2 | Your work email | Work |
| 3 | A disposable email address | Sign-ups, free trials, one-time codes |
For that third tier, using disposable email addresses is far more effective than maintaining a permanent “junk” inbox. Temporary interactions never generate lasting spam because the address itself disappears. Our guide on using disposable email for signups walks through the exact process.
2. Choose the Best Email for Privacy and Security
When it comes to privacy, email providers differ wildly. Standard providers like Gmail and Outlook do not encrypt your mail end to end, so the provider holds it in a form it can read.
The best email accounts for privacy use end-to-end encryption by default, meaning even the email provider can’t read your messages. The best known today are Proton Mail (based in Switzerland, with end-to-end encryption) and Tuta, formerly Tutanota (made in Germany, with encrypted email, calendar and contacts). Skiff Mail, once a third option, joined Notion and ended its service in 2024.
For the best email privacy and security setup, pair one of these encrypted providers with a disposable email service like Pokemail for signups and throwaway interactions. Your encrypted provider handles sensitive messages. Disposable email handles everything else, keeping your address hidden.
3. Enable Two-Factor Authentication
Your email account is the master key to your digital life. If someone gains access to your inbox, they can reset passwords for your banking, social media, and every other service that uses email-based recovery. Protect it with two-factor authentication, preferably an authenticator app like Google Authenticator, Authy, or a hardware key like YubiKey rather than SMS, which is vulnerable to SIM-swapping attacks.
This takes five minutes to set up and sharply reduces the risk of account compromise, even if your password is leaked in a data breach.
4. Disable Remote Image Loading
Email images frequently contain tracking pixels, invisible one-by-one pixel images that notify the sender when you open their message. A single tracking pixel can reveal your IP address, your device type, the time you read the email, and your approximate geographic location.
Most email clients let you disable automatic image loading and display images only when you explicitly choose to. In Gmail, open Settings, then See all settings, and under Images select “Ask before displaying external images.” Apple Mail users should enable Mail Privacy Protection under Settings, then Mail, then Privacy Protection. Outlook users can go to Settings and disable automatic image loading. Thunderbird users should check Settings, then Privacy and Security, and uncheck “Allow remote content in messages.”
This single change blocks most email open tracking. Our guide to the email tracking pixel explains how a pixel works and how to block it.
5. Use Disposable Addresses for One-Time Interactions
Anytime a website asks for your email and you don’t plan to use the service long-term, use a temporary address. This prevents your email from appearing in future data breaches and eliminates the marketing follow-up.
The habit takes about a week to build. Before entering your email anywhere, ask yourself “will I need this account next month?” If the answer is no, use a throwaway email instead. If the answer is “maybe,” start with a disposable address and upgrade to your real email later if the service proves valuable.
Over time, this simple habit drastically reduces the number of places your real email address exists in databases across the internet. We also have a detailed guide on choosing a safe temp email service.
6. Check Before You Click
Phishing emails have become incredibly sophisticated. Modern phishing campaigns use AI-generated content that perfectly mimics the tone and formatting of legitimate companies. Before clicking any link in an email, hover over it to see the actual URL destination. Legitimate companies use their own domains for links. If the URL points to an unfamiliar domain, uses URL shorteners, or has subtle misspellings (like “arnazon.com” instead of “amazon.com”), don’t click it.
When in doubt, navigate to the website directly by typing the address into your browser rather than following the link in the email. This one habit prevents the majority of successful phishing attacks.
7. Review App Permissions Regularly
Third-party apps connected to your email account, including newsletter tools, CRM integrations, calendar sync services, and browser extensions, can often read your entire inbox. Many people grant these permissions once and forget about them, leaving dozens of third-party apps with ongoing access to their email.
Review these permissions quarterly and revoke access for anything you no longer use. In Gmail, check myaccount.google.com/permissions. For Microsoft accounts, check account.microsoft.com/privacy. Apple users should go to Settings, then their name, then Sign-in and Security.
You’ll likely find apps you forgot you connected, and some may have been compromised since you authorized them.
8. Encrypt Sensitive Emails
For truly confidential communication, use end-to-end encryption. If you’ve switched to ProtonMail or Tuta as your primary provider, encryption is already built in. For Gmail or Outlook users, browser extensions like Mailvelope add PGP encryption capability to your existing webmail interface.
At minimum, never send passwords, financial account numbers, government ID numbers, or medical information in plain email. These messages pass through multiple servers in transit and could be intercepted or stored indefinitely. Use a secure file-sharing service or an encrypted messaging app for sensitive data instead. For a talk you would rather not keep, there are private chat rooms that open with a secret word.
9. Be Cautious With Public Wi-Fi
Reading email on public Wi-Fi without a VPN means your traffic passes through a network you don’t control. While HTTPS protects the content of your messages, the network operator can still see which email service you’re connecting to, when you connected, and how long you spent. On poorly secured networks, more sophisticated attacks are possible.
Coffee shops, airports, and hotel networks are particularly risky because they’re high-traffic environments where attackers can blend in. Use a reputable VPN whenever you access email on networks you don’t own. The VPN encrypts everything between your device and the VPN server, making your traffic opaque to anyone else on the local network.
This applies to mobile devices too. Connecting to public Wi-Fi on your phone and opening your email app exposes the same information. Either use cellular data or activate your VPN first.
10. Audit Your Email Footprint
Search for your email address on HaveIBeenPwned.com to see if it appears in known data breaches. The site lists over 17 billion compromised accounts. If your address appears, change your password immediately and enable two-factor authentication if you haven’t already.
Beyond breach checking, do a quick search for your email address in Google. You might be surprised where it shows up publicly: old forum posts, social media profiles, WHOIS records for domains you own, cached web pages, or public code repositories. Each public appearance is a vector for spam and targeted phishing.
Set a calendar reminder to check both HaveIBeenPwned and your Google search results every three months. Staying aware of your email footprint is the first step to controlling it.
7 Ways to Protect Your Email Privacy
Nearly every online account you own is tied to a single email address. When that address gets exposed, sold, or breached, the fallout spreads fast: targeted phishing, identity theft, and a flood of spam that never stops. Each of the seven ways below protects that one address, and several build on the tips above.
1. Use Disposable Email for Non-Essential Signups
The most effective way to protect your email privacy is to stop giving out your address when you don’t need to. Most websites that ask for your email only need it to send a single verification code. They don’t need ongoing access to your inbox.
Whenever a website asks for your email and you’re not planning to maintain an ongoing relationship with that service, use a temporary address from Pokemail. You’ll receive the verification code or download link you need, and when the temporary inbox expires, there’s no address left for anyone to spam, sell to data brokers, or expose in a data breach.
The habit takes about a week to build. Before entering your real email anywhere, ask: “Will I need this account next month?” If the answer is no, use a disposable address. If the answer is maybe, start with a temporary address and switch to your real email later if the service proves valuable. Our step-by-step guide walks through the exact process for major platforms.
2. Never Post Your Real Email Publicly
Automated scrapers continuously crawl websites, forums, social media profiles, GitHub repositories, and public directories for email addresses. Any address that appears in plain text anywhere on the internet will eventually end up on spam lists, often within days.
This happens more often than people realize. A Stack Overflow answer with your email in the signature, a personal website with a contact address in the footer, an old forum post from a decade ago, or a WHOIS record for a domain you registered. Each of these is a vector for spam, phishing, and social engineering.
When you need to share contact information publicly, use a contact form instead of a plain email address. If that’s not an option, use a dedicated public-facing address that’s separate from your primary inbox. Some people use a permanent email alias for this purpose, which can be disabled if it starts attracting spam.
3. Block Email Tracking Pixels
Tip 4 above shows how to stop images loading in Gmail, Apple Mail, Outlook and Thunderbird. For newsletters and marketing emails you want to read without being tracked, using a disposable email address ensures the tracking data never connects to your real identity.
4. Train Your Spam Filter
Gmail, Outlook, Yahoo, and most major providers include sophisticated spam filtering powered by machine learning. Make sure yours is actually enabled and configured properly, as some settings changes can inadvertently weaken it.
More importantly, actively train your spam filter by marking spam emails as spam rather than just deleting them. Each time you mark a message as spam, you’re feeding data into the filter’s model, helping it catch similar messages in the future.
Check your spam folder occasionally to rescue legitimate emails that were incorrectly flagged, and mark those as “not spam” to improve accuracy in both directions.
5. Create Smart Filtering Rules
Most email clients let you create rules that automatically sort, archive, or delete messages based on sender, subject line, or content. This is especially useful for managing the gray area between legitimate email and spam, meaning messages that technically aren’t spam but that you didn’t ask for and don’t want.
Set up rules to catch common patterns. Emails from unknown senders containing aggressive sales language can go straight to a filtered folder. Order confirmations can auto-sort into a shopping folder. Newsletter subscriptions can funnel into a reading folder that you check once a week instead of having them interrupt your primary inbox throughout the day.
Aggressive filtering is always better than a cluttered inbox. You can check the filtered folder if you’re expecting something, but in practice, you’ll find that most filtered messages didn’t deserve your attention.
6. Use a Separate Address for Shopping
Online purchases require an email for order confirmations and shipping notifications. Creating a dedicated email address just for e-commerce keeps all retail correspondence in one place, separate from your personal and professional inboxes.
This also limits the impact when a retailer suffers a data breach. If your shopping email appears in a breach, your personal email and its connected accounts remain untouched. You change one password and move on instead of worrying about cascading access.
When a retailer’s marketing becomes excessive, you only need to manage one inbox rather than hunting down subscriptions scattered across your primary address. For long-term shopping accounts, a permanent email alias gives you the same isolation with the added ability to disable a specific alias if it starts attracting spam.
7. Audit Your Email Footprint Regularly
Tips 7 and 10 above cover the check of breaches, a search for your address and the apps connected to your inbox. Set a calendar reminder to run this audit every three months. The five minutes it takes could prevent a cascade of problems.
What About Unsubscribe Links?
Legitimate businesses are required to honor unsubscribe requests under both the US CAN-SPAM Act and the EU’s GDPR. In the US, the FTC’s CAN-SPAM guide says a sender must honor an opt-out request within 10 business days.
However, clicking “unsubscribe” in a message from an unknown or suspicious sender can actually confirm that your address is active and monitored, which can lead to more spam from other sources using the same list. The safer approach for suspicious emails: mark them as spam in your email client and let the provider handle it.
Your Legal Rights
If you’re in Europe, GDPR gives you powerful email privacy rights. You can request that any company delete all data they hold about you, including your email address and behavioral profile. The company must answer within one month, a period it may extend by two further months where needed (GDPR Article 12). In practice, the unsubscribe link is faster for stopping individual emails, but a formal data deletion request (sometimes called a “right to erasure” request) removes your address from their database for good.
In the US, the CAN-SPAM Act requires commercial emails to include a working unsubscribe mechanism. California’s CCPA, as amended by the CPRA, gives California residents the right to know what personal information a business collects and the right to delete it, with some exceptions.
Regardless of your jurisdiction, the preventive approach, using disposable email addresses for non-essential signups, is always more effective than any legal remedy after the fact. It’s far easier to prevent your email from entering a database than to get it removed later.
The Principle Behind All of These
Email privacy isn’t a single action. It’s a set of habits that build on each other. The combination of disposable email for temporary interactions, aliases for ongoing relationships, encrypted providers for sensitive messages, strong authentication, and regular auditing creates a layered defense that makes your inbox much harder to compromise or exploit.
The most important step is starting. Start with the easiest wins: disposable email for signups and tracking pixel blocking. Pick two or three tips from this list and implement them today. You can add the rest over time. For the case for a throwaway address, see what a throwaway email is and how to make one.
Free temporary email in one click. No registration, no tracking. Auto-deletes in 60 minutes.
Frequently Asked Questions
What is the best email for privacy and security?
For maximum email privacy, use an encrypted provider like Proton Mail or Tuta for personal correspondence. For signups and one-time interactions, use disposable email services like Pokemail to avoid giving out your real address entirely. The combination of encrypted email for important messages and disposable email for everything else provides comprehensive protection. For signups and temporary interactions, pair your encrypted provider with a disposable email service to keep your real address completely hidden.
What is the best email account for privacy?
ProtonMail and Tuta are widely considered the best email accounts for privacy because they offer end-to-end encryption by default and are based in countries with strong privacy laws. For everyday browsing and signups, pair your private email with a disposable email service to minimize your exposure.
How do I stop companies from tracking my email?
Disable automatic image loading in your email client settings. This blocks tracking pixels that report when you open messages. In Gmail, open Settings, then See all settings, and under Images select Ask before displaying external images. Apple Mail has built-in Mail Privacy Protection that handles this automatically.
Should I use different emails for different purposes?
Yes. Maintain at least three tiers: one private encrypted email for personal correspondence, one for work, and disposable addresses for online signups and services. This limits damage from any single breach and keeps marketing spam away from your important inboxes.
What is the best way to protect email privacy?
The single most effective step is to never give out your real email address when you don't need to. Use a disposable email service like Pokemail for signups, downloads, and any service you're unsure about. Combined with an encrypted email provider, spam filters, and two-factor authentication, this prevents most email privacy issues before they start.
Does unsubscribing from spam actually work?
For legitimate businesses, yes. In the US, the CAN-SPAM Act requires a sender to honor an opt-out request within 10 business days, and in the EU the GDPR gives you the right to object to direct marketing at any time. For suspicious or unknown senders, clicking unsubscribe can confirm your address is active and lead to more spam. Mark those as spam instead and let your email provider handle it.
How do I know if my email has been compromised?
Check HaveIBeenPwned.com with your email address to see if it appears in known data breaches. The site lists over 17 billion compromised accounts. If your address appears, change your password immediately and enable two-factor authentication.
Sources
- Proton Mail proton.me
- Tuta tuta.com
- CAN-SPAM guide ftc.gov
- GDPR Article 12 gdpr-info.eu
- CCPA oag.ca.gov
What this page says of another service comes from that service's own pages, and what it says of Pokemail from the service itself, checked on November 14, 2026. How we write and check our posts.
Email Tracking Pixel: What It Is and How to Block It
An email tracking pixel is a hidden image that tells the sender you opened an email. What it reveals and how to block it in Gmail, Outlook and Apple Mail.
How to Stop Spam Emails: 7 Steps That Work
How to stop spam emails: mark, block and unsubscribe in Gmail, Outlook, Yahoo and on iPhone, report what is left, then prevent new spam with a burner email.
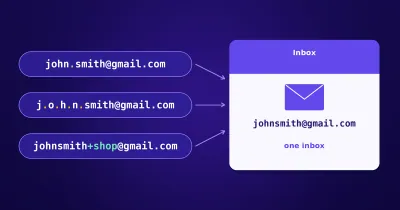
The Gmail Dot Trick and Plus Addressing: Do Dots Matter in Gmail?
How Gmail treats dots and plus tags in an address, how to use them to sort mail and spot leaks, and why neither one hides your real address.